SIEM

24/7 monitoring of your IT system's security by a SOC: prevention, detection, analysis and fast response to security incidents

Cybersecurity does not stop once protection mechanisms are in place. Threats are constantly evolving, attacks are relentless, and detecting an incident can take weeks without active monitoring in place. Econocom’s managed SOC provides continuous 24/7 monitoring of all your environments, physical, virtual, network, databases and business applications, from our resilient, certified in-house Security Centres, with international coverage. 

  • Econocom's in-house Security Centre: 24/7, resilient, sovereign and certified, with international coverage
  • Monitoring of every type of resource: physical, virtual, network, databases, business applications
  • Compatible with a wide range of market tools: Palo Alto Cortex, Cisco, CrowdStrike, Trend Micro, HarfangLab...

Managed SIEM

Prevention, detection, remediation and incident management: a comprehensive SOC to protect your entire IT system

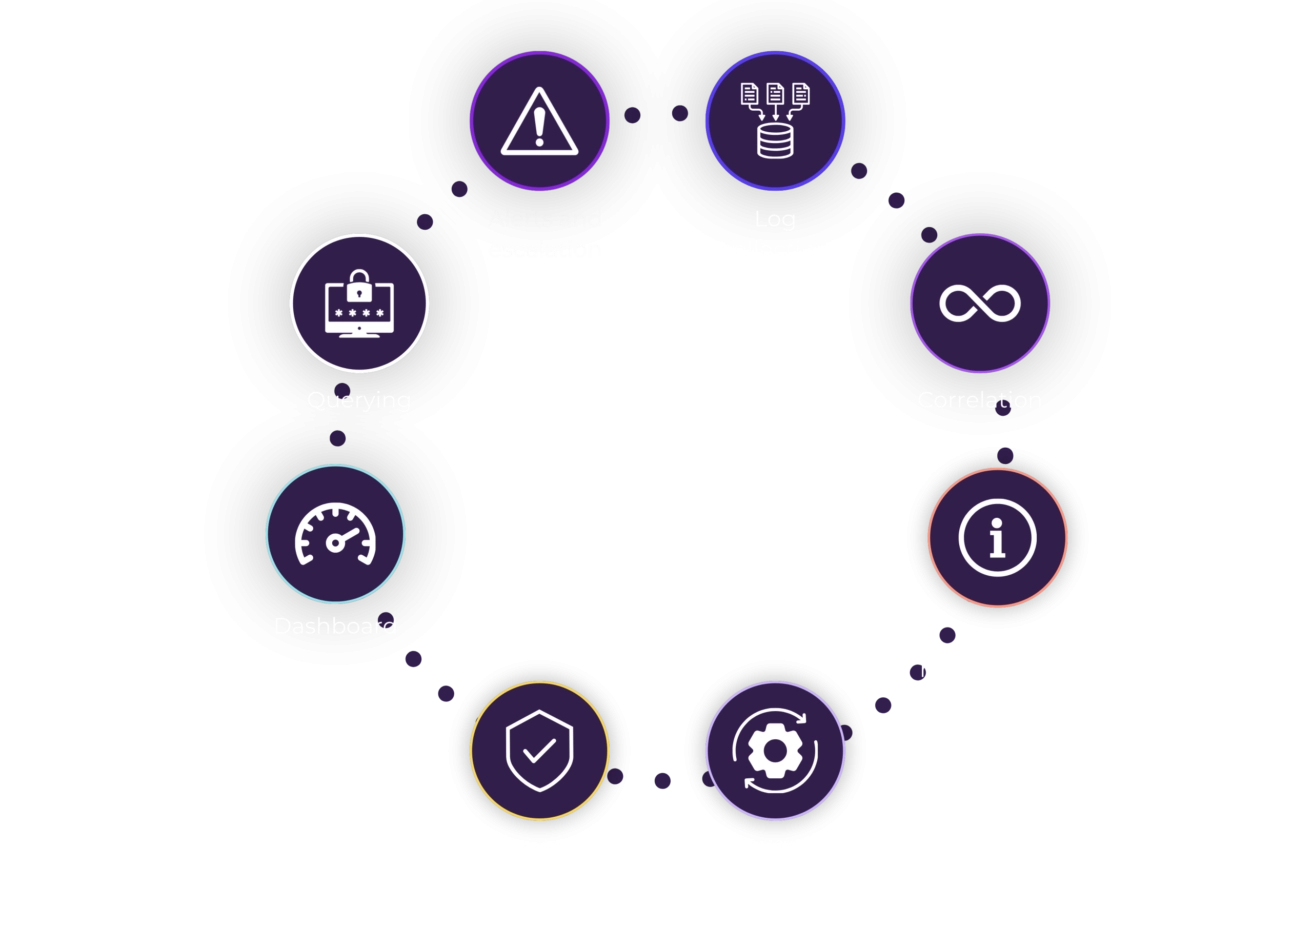
  • Monitoring of every type of resource: physical, virtual, network, databases and applications

    Econocom’s SOC continuously monitors every resource in the IT system: physical equipment, virtual environments, network equipment, databases and business applications. This exhaustive coverage guarantees that no component of the information system escapes monitoring. 

  • Automatic aggregation and correlation of events, across all your platforms

    The SIEM automatically collects and correlates security events from all monitored components. Multi-source correlation makes it possible to detect attack patterns that would not be visible when analysing each source in isolation. 

  • Remote remediation and escalation

    When an incident is confirmed, Econocom’s SOC teams trigger remediation procedures: isolating compromised systems, blocking malicious communications and escalating to operational teams according to defined protocols. 

  • Security incident management by a dedicated Security Centre

    Econocom’s SOC (Security Operations Center), operated 24 hours a day, 7 days a week, handles the qualification, management and resolution of security incidents. Escalation to third parties is possible depending on the nature and severity of incidents. 

  • A wide range of market and in-house tools: Palo Alto Cortex, Cisco, CrowdStrike, Trend Micro

    Econocom’s SOC relies on a selection of market tools, Palo Alto Cortex, Cisco, CrowdStrike, Trend Micro, complemented by in-house tools developed by Econocom. This combination guarantees optimal threat coverage and the ability to adapt to each client environment’s specifics. 

Faster detection, a more effective response and IT teams freed from monitoring duties.

  • Better anticipation and automation for a faster response

    Automatic event correlation and automation of initial remediation actions make it possible to anticipate incidents and reduce the time between detection and response.

  • Effective 24x7 coverage that lightens the load on internal resources

    Econocom's SOC provides continuous monitoring 24 hours a day, 7 days a week, freeing internal IT teams from the constraint of security on-call duties and allowing them to focus on higher-value projects.

  • Cost optimisation without compromising security

    Outsourcing security monitoring to an industrialised SOC provides a high level of expertise and coverage at a lower cost than an equivalent in-house SOC.

  • Improved availability and resource management

    Real-time visibility over incidents and security dashboards make it possible to better manage resources dedicated to security and prioritise actions according to the criticality of threats.

Frequently Asked Questions

  • A SOC (Security Operations Center) is an operational centre dedicated to monitoring, detecting and responding to cybersecurity incidents. Econocom operates its own SOC, available 24/7, with international coverage and highly certified expertise.

  • The SIEM (Security Information and Event Management) is the technology tool that collects, correlates and analyses security events. The SOC is the human organisation that uses the SIEM and other tools to detect, investigate and respond to incidents. Econocom offers both, combined in a managed offer.

  • Econocom's SIEM relies on a wide range of market tools, Palo Alto Cortex, Cisco, CrowdStrike, Trend Micro, complemented by in-house tools developed internally. The choice of tools deployed for each client is suited to their environment and specific needs.

  • Setting up a managed SOC begins with an assessment of the existing environment: the scope to be monitored, the maturity of security tools in place and the expected service levels. On this basis, our experts define the monitoring scope and suitable SLAs. Let's talk to assess your situation.

Talk to an Econocom expert

Entrust the monitoring of your IT security to Econocom's SOC: 24/7, international coverage, leading market tools and an in-house Security Centre.

Discuss your project